GitLab CVE-2026-19478: CVSS 9.4 Critical Vulnerability Explained
Detailed technical breakdown and remediation guide for CVE-2026-19478, a critical CVSS 9.4 unauthenticated GraphQL vulnerability affecting GitLab CE and EE.
Security intelligence, vulnerability research, and best practices from the VAPT Insights team.

Detailed technical breakdown and remediation guide for CVE-2026-19478, a critical CVSS 9.4 unauthenticated GraphQL vulnerability affecting GitLab CE and EE.

A practical guide to .env security, accidental GitHub exposure, AI-agent access, client-side environment variables, secret rotation, and safer application architecture.

Detailed technical breakdown of CVE-2026-71319 / GHSA-279x-mwfv-vcqv in @nuxt/devtools, enabling unauthenticated remote command execution in development mode.

Discover the top 25 website security misconfigurations in 2026 — from exposed .env files to AI API flaws. With fixes, code snippets & a manual testing checklist.

Learn what HTTP security headers are, why they matter, essential headers like CSP, HSTS, X-Frame-Options, and how to verify your website's security posture.

What the reported Bank of Baroda cybersecurity incident teaches organizations about DPDP Act compliance, email security, and building a real security posture beyond paperwork.

Ensure your website is prepared for India's Digital Personal Data Protection (DPDP) Act. Use this 25-point technical and compliance checklist to identify gaps and improve your privacy posture.

A developer's guide to the DPDP Act 2023. What problems it solves and how to check your compliance readiness without talking to sales or entering a credit card.
Discover why static dependency trackers are not enough for supply chain security. Learn how active SBOM tracking protects against nested vulnerabilities and compliance breaches.

Static headers checkers are great for quick checks, but they fail at continuous protection. Learn how active monitoring, SSL analysis, and webhook notifications safeguard your site.

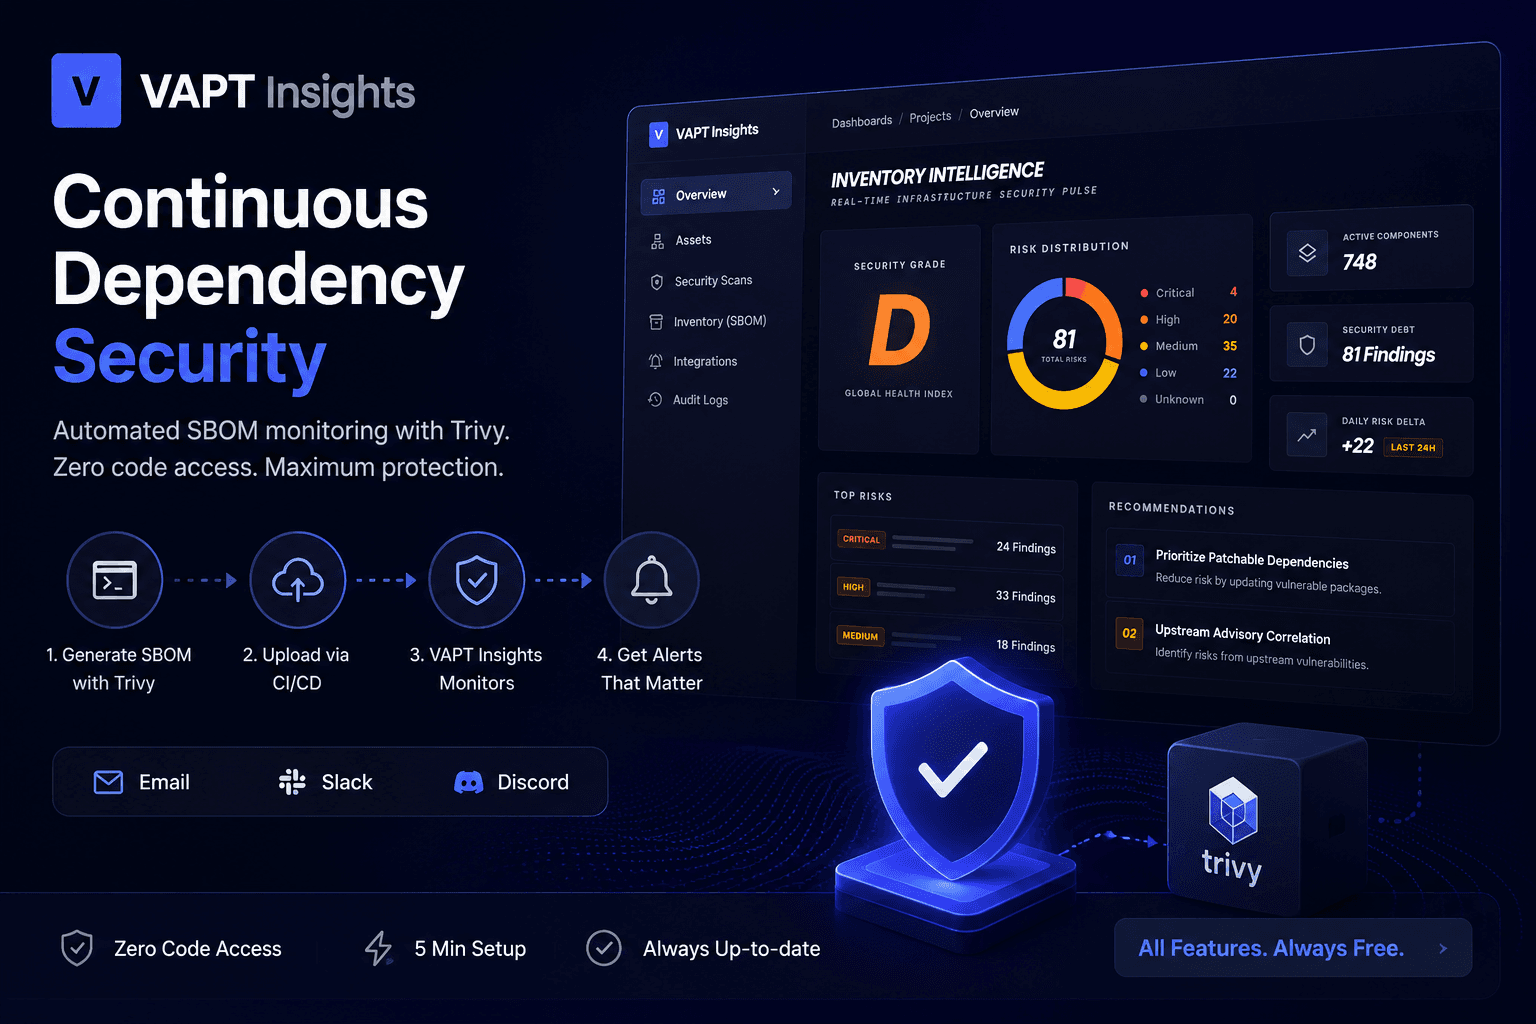
Learn how to generate SBOMs using Trivy and continuously monitor dependency vulnerabilities with VAPTInsights. Secure your software supply chain with automated CI/CD integration and zero code access.

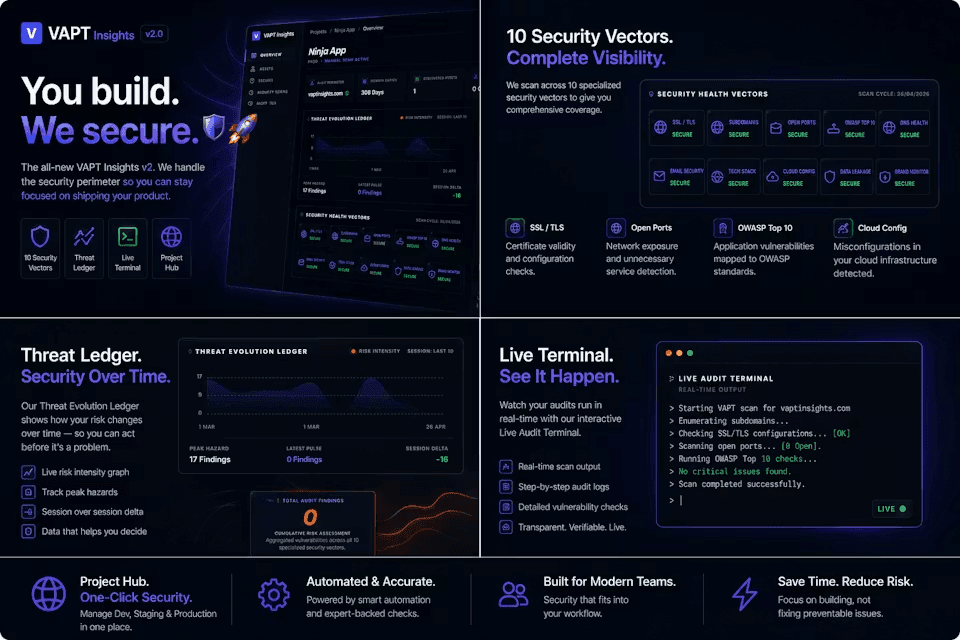
We just launched the all-new VAPT Insights v2.0. Handle your security perimeter and protect your SaaS, subdomains, SSL, and network ports in a single view.

Learn how to add a Content Security Policy (CSP) in a Next.js application step-by-step. Discover why CSP is vital, common directives, and how to verify it.

Free web app security scanner by VAPTInsights. Find & fix vulnerabilities in 1 click - no cost, no expertise needed. Protect against OWASP Top 10 risks

Enhance your DevOps pipeline with VAPT. Learn how integrating VAPT into your SDLC strengthens security, reduces costs, and boosts software quality.

Discover how VAPT (Vulnerability Assessment and Penetration Testing) helps detect hidden threats like SQL injections and XSS. Learn how vaptinsights.com

Learn why Vulnerability Assessment and Penetration Testing (VAPT) is essential for every business. Discover how VAPT protects your data, builds customer trust